
zizmor
Static analysis for GitHub Actions (and more)
INSTALLATION
$ pacman -S zizmor$ zypper install zizmor$ nix-env -iA nixos.zizmor$ cargo install --locked zizmor$ brew install zizmor$ sudo port install zizmor$ pip install zizmor$ pipx install zizmor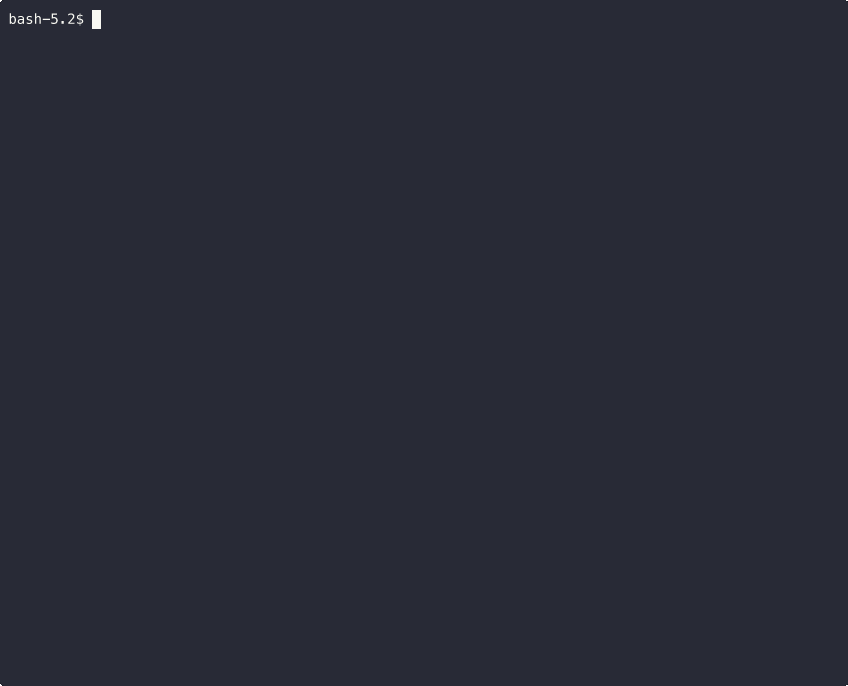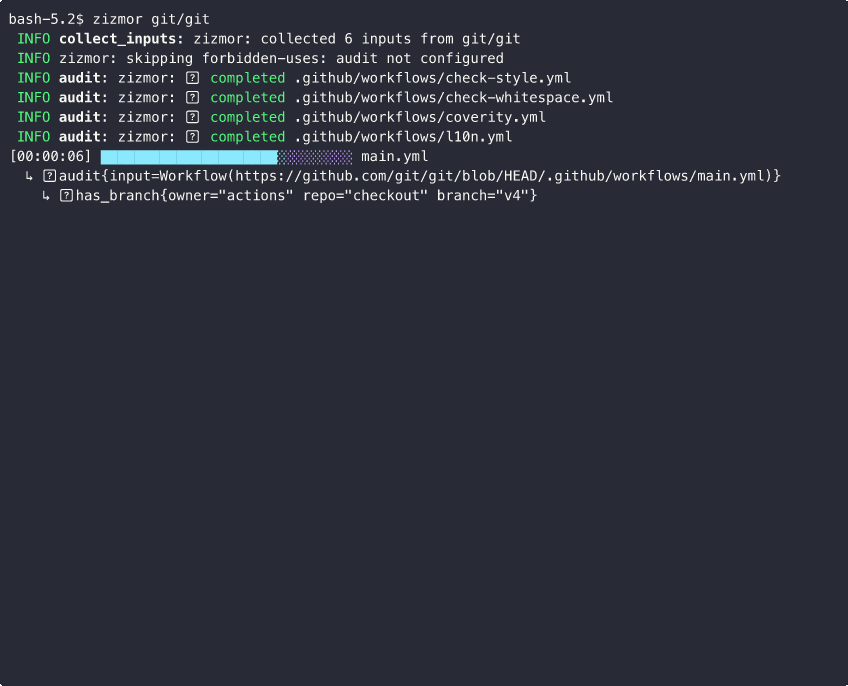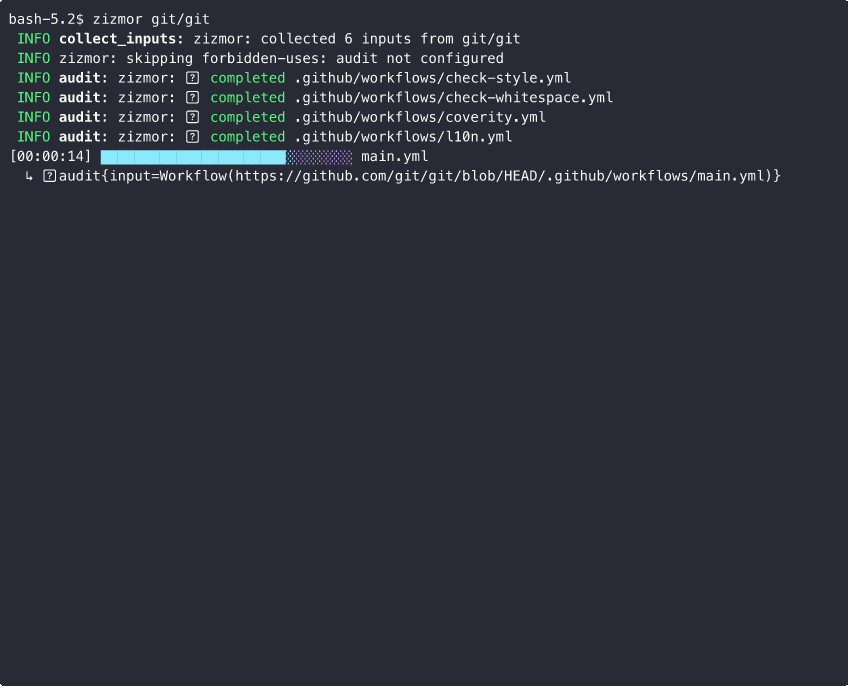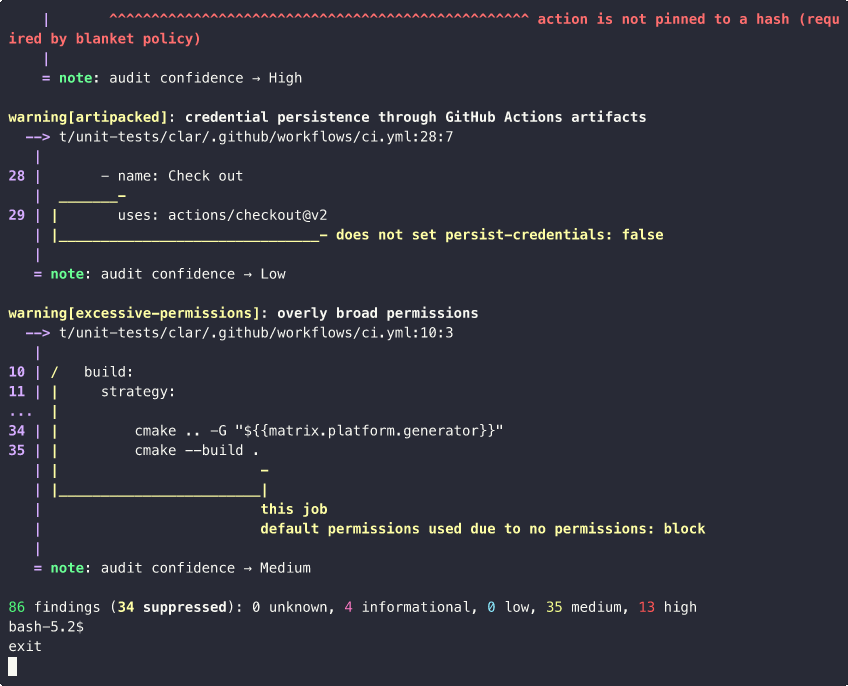
DESCRIPTION
zizmor is a static analysis and security auditing tool designed specifically for GitHub Actions and CI/CD configurations.
It detects critical vulnerabilities like template injections, excessive token permissions, unpinned actions, and credential leaks before they reach production.
Seamlessly integrates into local terminals, pre-commit hooks, editors via LSP, and CI pipelines to enforce robust supply-chain security.
DETAILS
- Repository
- zizmorcore/zizmor (2026-11-19)
- Website
docs.zizmor.sh/
- Author
- zizmorcore
- License
- MIT
- Category
- DevOps & Cloud
- Language
- Rust
- Platforms
- Linux, macOS, Windows
- Version
- v1.32.0 (2026-11-02)
- Repo Age
- 2 years old
STAR HISTORY
TAGS
SEE ALSO
- Featured in GitHub and GitLab from the terminal
- Featured in Code analysis tools for the terminal
BADGE
Maintain zizmor? Add this badge to your README: listings that link back are marked verified and ranked first in the directory. It's checked once a day.
[+] show code[−] hide code
[](https://cli.masoko.net/tools/zizmor/)<a href="https://cli.masoko.net/tools/zizmor/"><img src="https://cli.masoko.net/badge/zizmor.svg" alt="zizmor on The Terminal Index"></a>COMMENTS
- No comments yet. Be the first.
to comment.
RELATED TOOLS
dive
GoA tool for exploring each layer in a docker image
★ 54.7K▲ 39DevOps & Cloud8 years old
lazydocker
GoThe lazier way to manage everything docker
★ 53.4K▲ 120DevOps & Cloud7 years old
restic
GoFast, secure, efficient backup program
★ 37.3K▲ 7DevOps & Cloud12 years old
k9s
GoKubernetes CLI To Manage Your Clusters In Style!
★ 35K▲ 69DevOps & Cloud7 years oldgws-cli
RustGoogle Workspace CLI — one command-line tool for Drive, Gmail, Calendar, Sheets, Docs, Chat, Admin, and more. Dynamically built from Google
★ 32.4K▲ 9DevOps & Cloud8 months old
ctop
GoTop-like interface for container metrics
★ 17.9K▲ 13DevOps & Cloud9 years old

